Interim management
Interim project leadership for initiatives that must not fail.
- How I bill
- Day allowances, agreed for a clearly defined phase.
AI management systems for regulated industry
AI brings new obligations. Information security, business continuity and validation are the existing ones. I build the management systems for them as one and make them audit-ready, with evidence an auditor accepts.
15 years at Bayer AG
30 minutes, confidential
Behind it sits the same question
Customer evidence, AI in the plant, an emergency plan or a validated system: in the end, a sound classification decides the effort. Five steps, the same in every field.
Step 01
What exactly is the subject?
System boundary, inventory, legal role. The step most often skipped, and the one behind most of the disputes that follow.
Key questions
For example An AI inventory that also captures the AI inside bought-in software.
Boundary and inventory
Step 02
How critical is it?
A defensible classification decides the effort for everything that follows. It legitimately removes work instead of treating everything as equally critical.
Key questions
For example Classification per AI system under the EU AI Act, protection needs per process, GAMP category per system.
Classification with rationale
Step 03
What follows from it, and what explicitly does not?
The result is a reasoned list, not a copy of the standard.
Key questions
For example A statement of applicability under ISO/IEC 42001 with a rationale for every control.
Reasoned list of obligations
Step 04
What does an auditor actually hold in their hands?
Specifications, tests, records, traceability. Only here does the material an auditor reviews come into existence.
Key questions
For example A chain of evidence from the intended purpose of an AI system to the test result.
Audit-ready documents
Step 05
How does it stay true?
Change control, effectiveness measurement, internal audits, action tracking. Without this step, everything before it decays within a year.
Key questions
For example A review cycle that notices when the purpose, data or model of an AI system changes, instead of a rush before the audit.
Audit cycle
Separate systems, one liability
What can go wrong, how likely is it, how severe would it be, and what can be done about it? I answer that in a way an auditor can recalculate.
Hover or tap a dot to see an example.
Initial riskAI-supported shift planning without involving the works council (high risk under Art. 6)(Likelihood 3 / Impact 4)
Residual risk after treatmentReasoned classification and a works agreement(Likelihood 1 / Impact 3)
Initial riskAI visual inspection in quality control without a written intended purpose(Likelihood 4 / Impact 4)
Residual risk after treatmentIntended purpose, classification and approval before use(Likelihood 2 / Impact 3)
Initial riskStaff enter company data into freely available AI tools(Likelihood 5 / Impact 3)
Residual risk after treatmentApproved tools, clear rules and AI literacy training(Likelihood 3 / Impact 2)
Initial riskRemote maintenance access without multi-factor sign-in directly at the filling line(Likelihood 4 / Impact 5)
Residual risk after treatmentJump host with zone separation per IEC 62443(Likelihood 2 / Impact 2)
Initial riskRestart after an outage only agreed verbally(Likelihood 2 / Impact 5)
Residual risk after treatmentRestart plan with a target time, rehearsed and kept current(Likelihood 1 / Impact 4)
Initial riskGaps in the audit trail of batch documentation(Likelihood 5 / Impact 2)
Residual risk after treatmentComplete chain of evidence, checked by regular sampling(Likelihood 3 / Impact 1)
Getting started
I start where the pressure is highest. First comes a clear baseline that shows what matters now and what can wait.
When AI is in use but nobody can say whether that is a problem.
You receive
So that you cantell any customer or auditor in one sentence which AI you use, how, and why that is permissible.
Discuss thisWhen you want to know how far your handling of AI is from a management system under ISO/IEC 42001.
You receive
So that you canknow what is missing for audit readiness, and what is not.
Discuss thisWhen it is unclear whether and how your company is covered.
You receive
So that you canprove whether and how you are covered, and name your obligations as management.
Discuss thisWhen customers demand evidence or an audit is coming up.
You receive
So that you candirect budget to the gaps that actually matter.
Discuss thisWhen nobody can say for sure how long production runs without ERP or control systems.
You receive
So that you candecide which outage is tolerable, and what happens when it occurs.
Discuss thisInterim leadership
Independent of any management system: for projects, transformations and ongoing responsibility that nobody in the company can carry right now.
Interim project leadership for initiatives that must not fail.
Ongoing part-time leadership for AI governance, information security and business continuity, as a virtual CISO (vCISO) for a defined period.
Clearly bounded initiatives with a named result and a date.
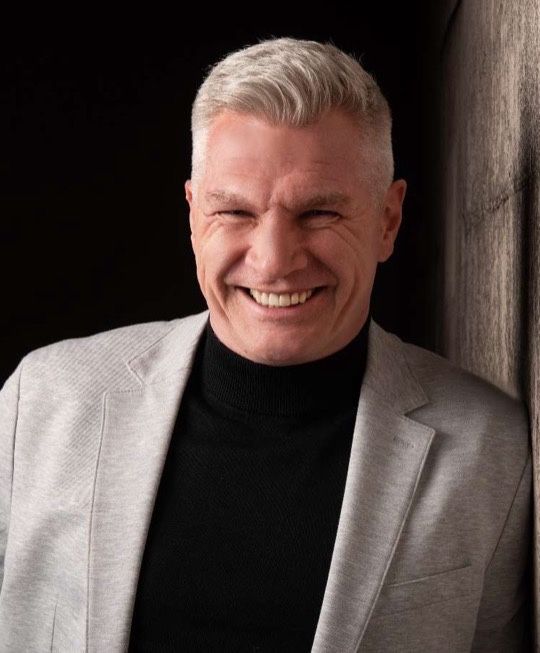
Who you will be talking to
I come from regulated pharmaceutical production: validation, automation and digitalisation where every change has to stand up to an inspector. Today I bring that way of working to AI, information security and business continuity.
Confidential, with no obligation. You will leave knowing where you stand.